Current evidence
Typed readiness RED/GREEN tests and active-runner inventory are current. Governed-bundle and browser evidence are accepted only after their executable reports are attached to the active spec.
The current program is governed by uat-production-readiness-convergence. Its first slice removes a concrete false-green: the platform harness no longer accepts arbitrary 4xx responses or starts an unowned repo-native dev service. The next launch-relevant slice must connect the constructed site-memory scanner/object-store dependencies to a persisted, tenant-scoped promotion consumer with browser, dependency-chaos, and container evidence.
Typed readiness RED/GREEN tests and active-runner inventory are current. Governed-bundle and browser evidence are accepted only after their executable reports are attached to the active spec.
CONDITIONAL. Historical Cloud SQL, certificate-pending, revision, and June screenshot statements below are predecessor evidence. Production database authority is Crunchy Bridge. No task counter, RTM rollup, static graph, screenshot, or endpoint liveness may upgrade the verdict.
This update folds in the 2026-06-27 production deployment: backend, CMS, and web are live on GCP Cloud Run run.app with Cloud SQL PG17, Upstash Valkey TLS, Secret Manager, and declarative Terraform IaC. The missed shared-table RLS step has also been completed on the live Cloud SQL database and wired into the backend. This is a production-runtime status addendum with no new screenshots; custom-domain browser proof, live public-domain /mcp cross-tenant proof, and UAT remain open.
An autonomous, collision-free hardening loop (running entirely clear of two other sessions' backend work) shipped six fixes to main (v0.11.76–v0.11.82) and deployed the accessible web fixes to production. Decision read: several genuine, previously-unnoticed defects — three stored-XSS sinks, a confirmed-exploitable admin eval-injection, a Next.js-16 production-breaking form bug, and a CI false-green — are now closed and (for the public web) live. This is a shipped code/security round (cited to PRs + tags), unit/component + curl-smoke tier; no operator screens changed, so the visuals on this page still stand.
This documentation-governance pass adds docs/SHOWCASE_GENERATION_GUIDE.md and updates the docs hub, manuals, review guide, README indexes, AGENTS.md, NEXT_STEPS.md, and RTM.md. Decision read: future refreshes now have one durable memo for keeping three audiences separate — prospect-facing showcase copy, operator-facing manual content, and evidence-facing executive review — instead of rediscovering that boundary in each regen.
A focused security/quality round landed on 2026-06-30 (PRs #162/#163/#164 to dev) that converts a previously partial / false-green security gate into a real, fail-closed release gate — and the now-functional scanners immediately surfaced and fixed two genuine production defects. These are shipped backend/security/tooling/governance changes (cited to PRs + governance evidence), local-gate tier; no operator screens changed, so the visuals on this page still stand. Decision read: the platform's claim to be "secure by gate" is now defensible — the gate actually runs all 5 scanners, blocks on real findings, and a secret can no longer be committed by accident — while hosted CI cost stays owner-gated by design.
This round is local security-gate + governance tier — no new browser screenshots (the 2026-06-16 captures + the 2026-06-21 governed payment screenshot still stand), no fabricated metrics. The gate is LOCAL (hosted CI cost stays owner-gated); NO new browser / UAT / deploy / live-provider / multi-region proof is claimed. Authority: .agents/specs/ISSUE_LOG.md (SECURITY-CI-RELEASE-GATE-001, SECRET-SCAN-GUARD-001), scripts/gosec-baseline.md, trivy.yaml, CONTRIBUTING.md, PRs #162/#163/#164.
An evidence-disciplined strategic read. Capability is strong and the platform is live; the binding constraint is external demand proof, not more features.
Owner decision 2026-06-30 — narrow to the NAELT victim-rights / NGO advocacy platform as the near-term launch beachhead, with the AI-agent-native layer (MCP discovery, agent-friendly SEO, A2UI authoring, GraphRAG) as the differentiation that rides on top. (Previously the scope spanned a horizontal "anyone builds a site" platform + 3 verticals + AI-native, all at once — too broad.)
An AI-agent-readable, self-manageable advocacy site that a small NGO team runs without engineers; the agent-native angle (MCP / agent-SEO) is genuinely "why now" and not me-too. The generic horizontal "build any site" framing is commodity (Webflow/Wix/Sanity/Strapi) and is NOT the wedge.
A real NGO (NAELT going live for real users) plus a second, non-affiliated NGO adopting; for the agent layer, an external AI agent discovering & operating a tenant via public /mcp.
The repo shows essentially zero external demand signal today — this is the central open question (a market fact, not provable from code).
| Bet | Evidence | Confidence | Kill / Risk Signal | Next Proof |
|---|---|---|---|---|
| Platform runs in prod (multi-tenant, live) | GCP Cloud Run + Crunchy live; GraphRAG live; security gate green | High | already boots | — (established) |
| AI-agent-native is the differentiation | MCP / .well-known, agent-config, A2UI, component-manifest, GraphRAG | Medium | no end-to-end "agent operates a real site" demo; public /mcp cross-tenant proof still open | a recorded "external AI agent discovers & operates a tenant via public /mcp" |
| NAELT beachhead has real, launchable demand | NAELT anchor tenant + advocacy content / seeds | Low–Medium | only one affiliated tenant; "live" today = boots, not "users using it" | NAELT live for real users on its custom domain, browser-proven end-to-end |
| "Anyone self-serves a site" has demand | Showcase demo + landing→/examples→signup funnel (shipped) | Low | no external signup / retention data | 5–10 external users complete signup→publish and still active after 7 days |
| Production is ready FOR USERS (not just running) | runtime live, BUT custom-domain browser / public-/mcp / UAT still open | Conditional | "live" is "process boots", not "customer in use" | one real external user, custom-domain, browser-proven end-to-end flow |
Custom-domain browser proof / public-/mcp cross-tenant proof / UAT sign-off still open; worker is a prod no-op; AGE & multi-region deferred; several specs are completed-local with hybrid / mock CMS-admin evidence. (These are PROOF-TIER, not missing implementation.)
The wedge was too dispersed (now narrowing to NAELT); no single signature "signal → action" closed-loop workflow; horizontal build-a-site lacks differentiation; no onboarding-retention UX evidence.
This is the HEALTHIEST area — security gate green, secret guard, observability IaC, one-command make setup, honest claim-capped docs. Engineering discipline is a genuine strength.
The BIGGEST hole — weak demand proof, no measurable adoption signal, distribution path unproven. The NAELT pivot is the move to convert this from an abstract platform into a provable beachhead.
Hold and harden + Narrow the wedge → ship NAELT(Not Invest — no external demand proof yet to justify more surface area; not Pause — it's live, real, technically strong.)
/mcp + agent-SEO proof that an external agent can discover & read the site (also closes SPTR-LIVE-WIRING-001's public-/mcp gap).Two batches landed on 2026-06-29 that materially strengthen the production-readiness posture of the live Cloud Run + Crunchy stack: a UAT de-stub / de-mock / wire-up pass and a set of platform-operations lanes (observability, live GraphRAG, asset scan-path, worker). These are shipped backend/security/operations changes (cited to PRs + spec evidence), not roadmap; no operator screens changed, so the visuals on this page still stand. Decision read: the platform is more honest and more defensible (a real production fail-open was closed, dead/over-stated surfaces were removed, AI search is live) — while monitoring-apply, worker-deploy, and the backup restore-drill remain explicit owner-gated next steps.
This pass is backend / security / operations + terraform validate tier — no new browser screenshots (the 2026-06-16 captures + the 2026-06-21 governed payment screenshot still stand), no fabricated metrics. Monitoring apply, worker deploy, and the backup restore-drill stay owner-gated; custom-domain browser proof, public-domain /mcp cross-tenant proof, AGE/GraphRAG-as-runtime, multi-region, and UAT remain unclaimed. Authority: .agents/specs/{uat-readiness-destub-wireup,cloud-run-observability,crunchy-bridge-db-migration,asset-object-storage-cloudrun,worker-runtime-deploy}/review.md, .agents/specs/{SPECS.md,NEXT_STEPS.md}, PRs #151/#155/#156/#158/#160.
The stakeholder docs now have a proper front door. The docs static host previously redirected its root straight to the English manual; it now serves a branded Documentation Hub (docs/index.html) that frames the three core documents (Manual EN/繁中, this Executive Review), presents the showcase tenant as the canonical live exemplar, and maps the eight platform capabilities — all in the same provisional NAELT CIS palette so the docs read as one product. This is a presentation/documentation enhancement (committed + Dockerfile-served), not a runtime or readiness change.
The tutoring plugin's previously contract-only media + consultant interfaces are now implemented end-to-end and live on production (Crunchy Bridge + Cloud Run) at www.austinchanglab.net/site/showcase/tutoring. This is a shipped, browser-proven capability (cited to PR #133 + spec evidence + Playwright screenshots).
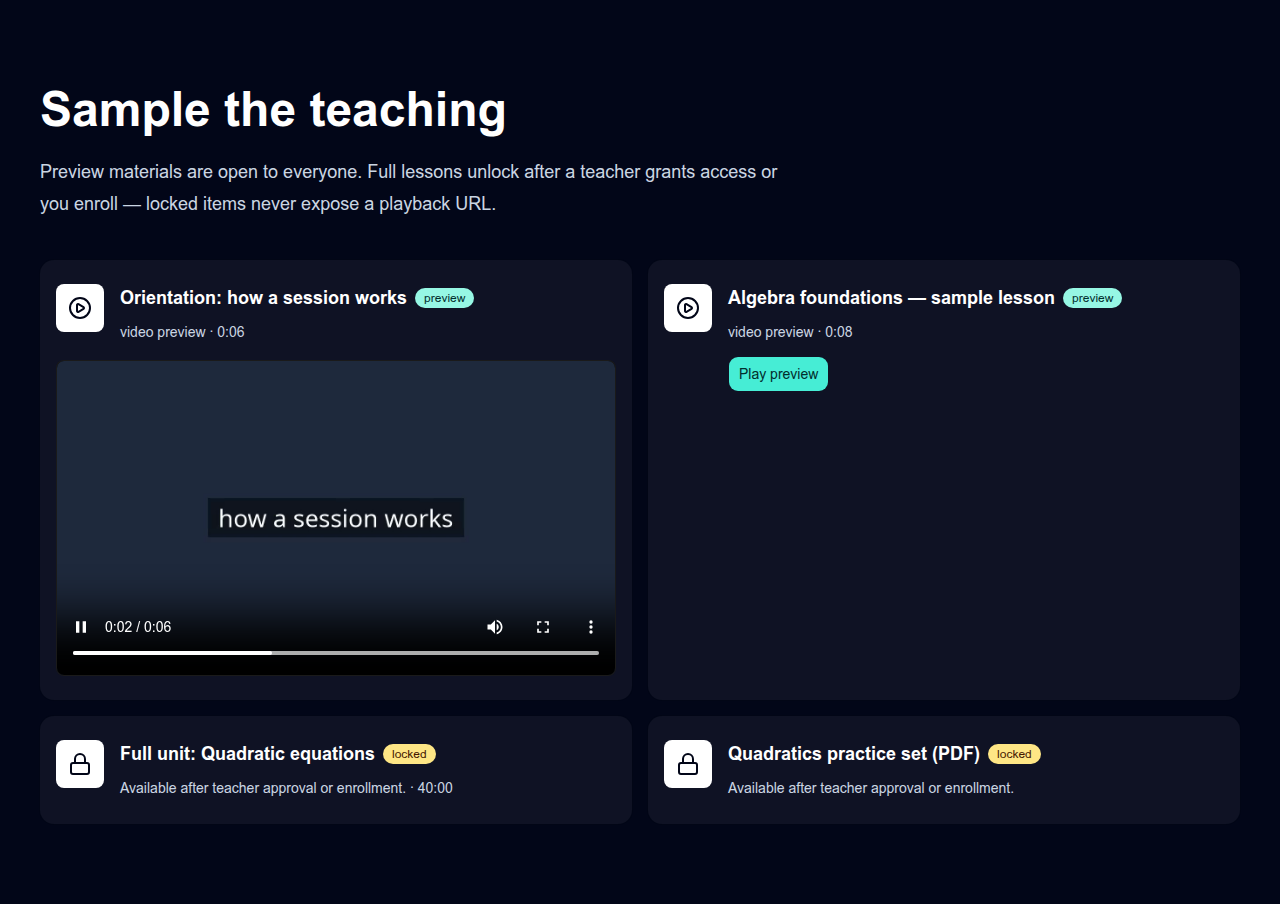
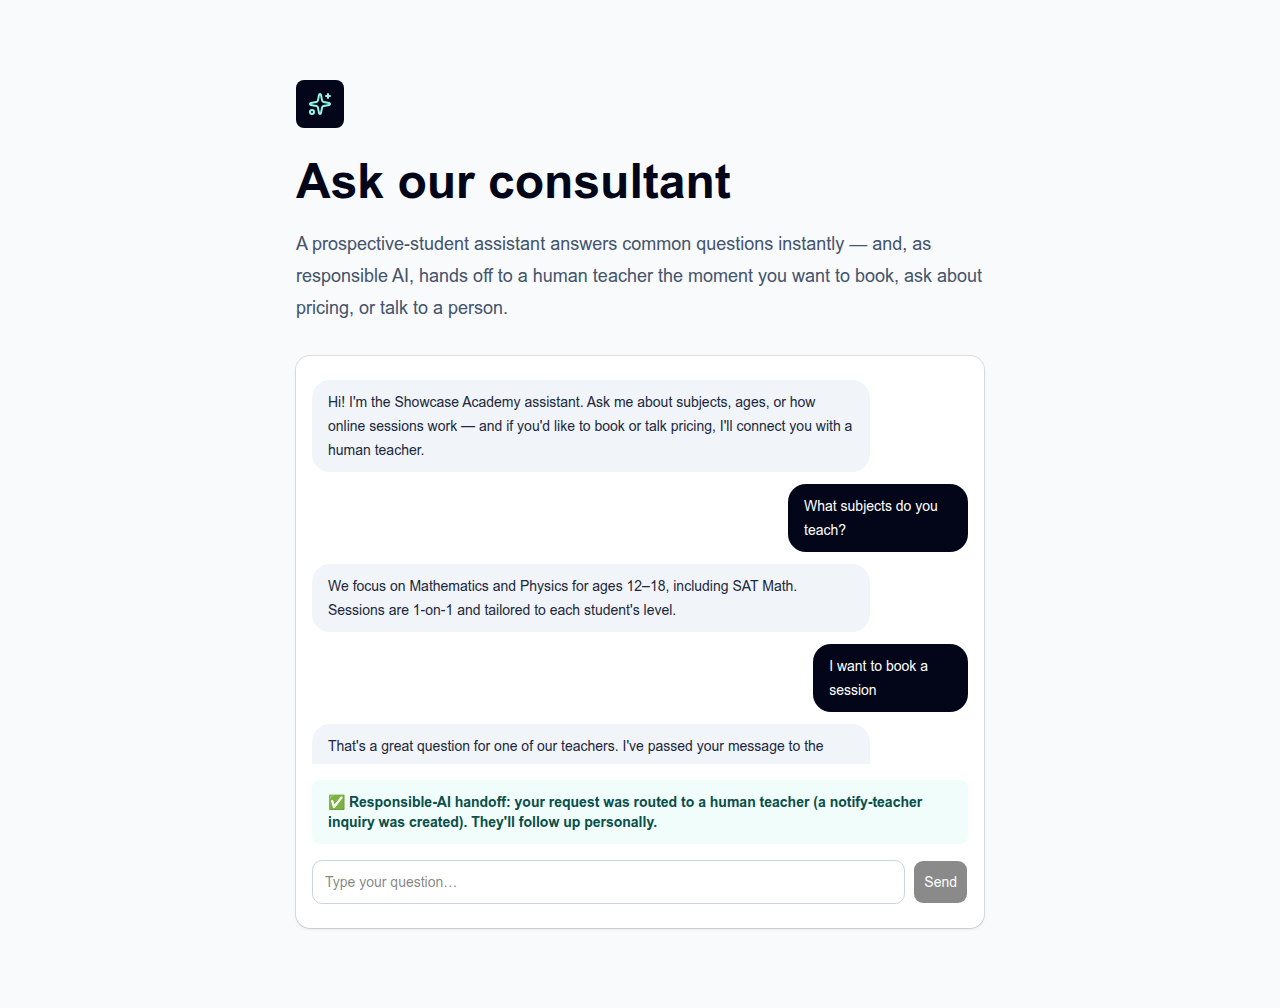
The owner-selected production topology is now the lower-ops managed path in ADR-DEPLOY-003: Cloud Run (backend + cms + web), Cloud SQL PG17 via Auth-Proxy unix socket, Upstash Valkey TLS, Google Secret Manager, and Cloud Run domain mappings for api/www/admin. This addendum updates executive readiness status; it does not claim fresh production visual approval.
A run of backend/test-tier prod-readiness lanes shipped as PRs against dev (#107/#108/#110/#111/#112/#113), reducing the codebase's mock-heavy / false-green / stub character with executable chaos & fail-closed coverage — and fixing one real wire-up bug found en route. These are shipped fixes (cited to PRs + spec evidence); no operator screens changed, so the visuals on this page still stand.
A generic, site-scoped, decoupled payment / donation / e-commerce module shipped as PR #86 against dev (payment-plugin). Donation is one purpose preset of a generic Payment* core. This is a shipped, browser-proven capability (cited to PR + spec + Playwright evidence), with a new donor-form screenshot.
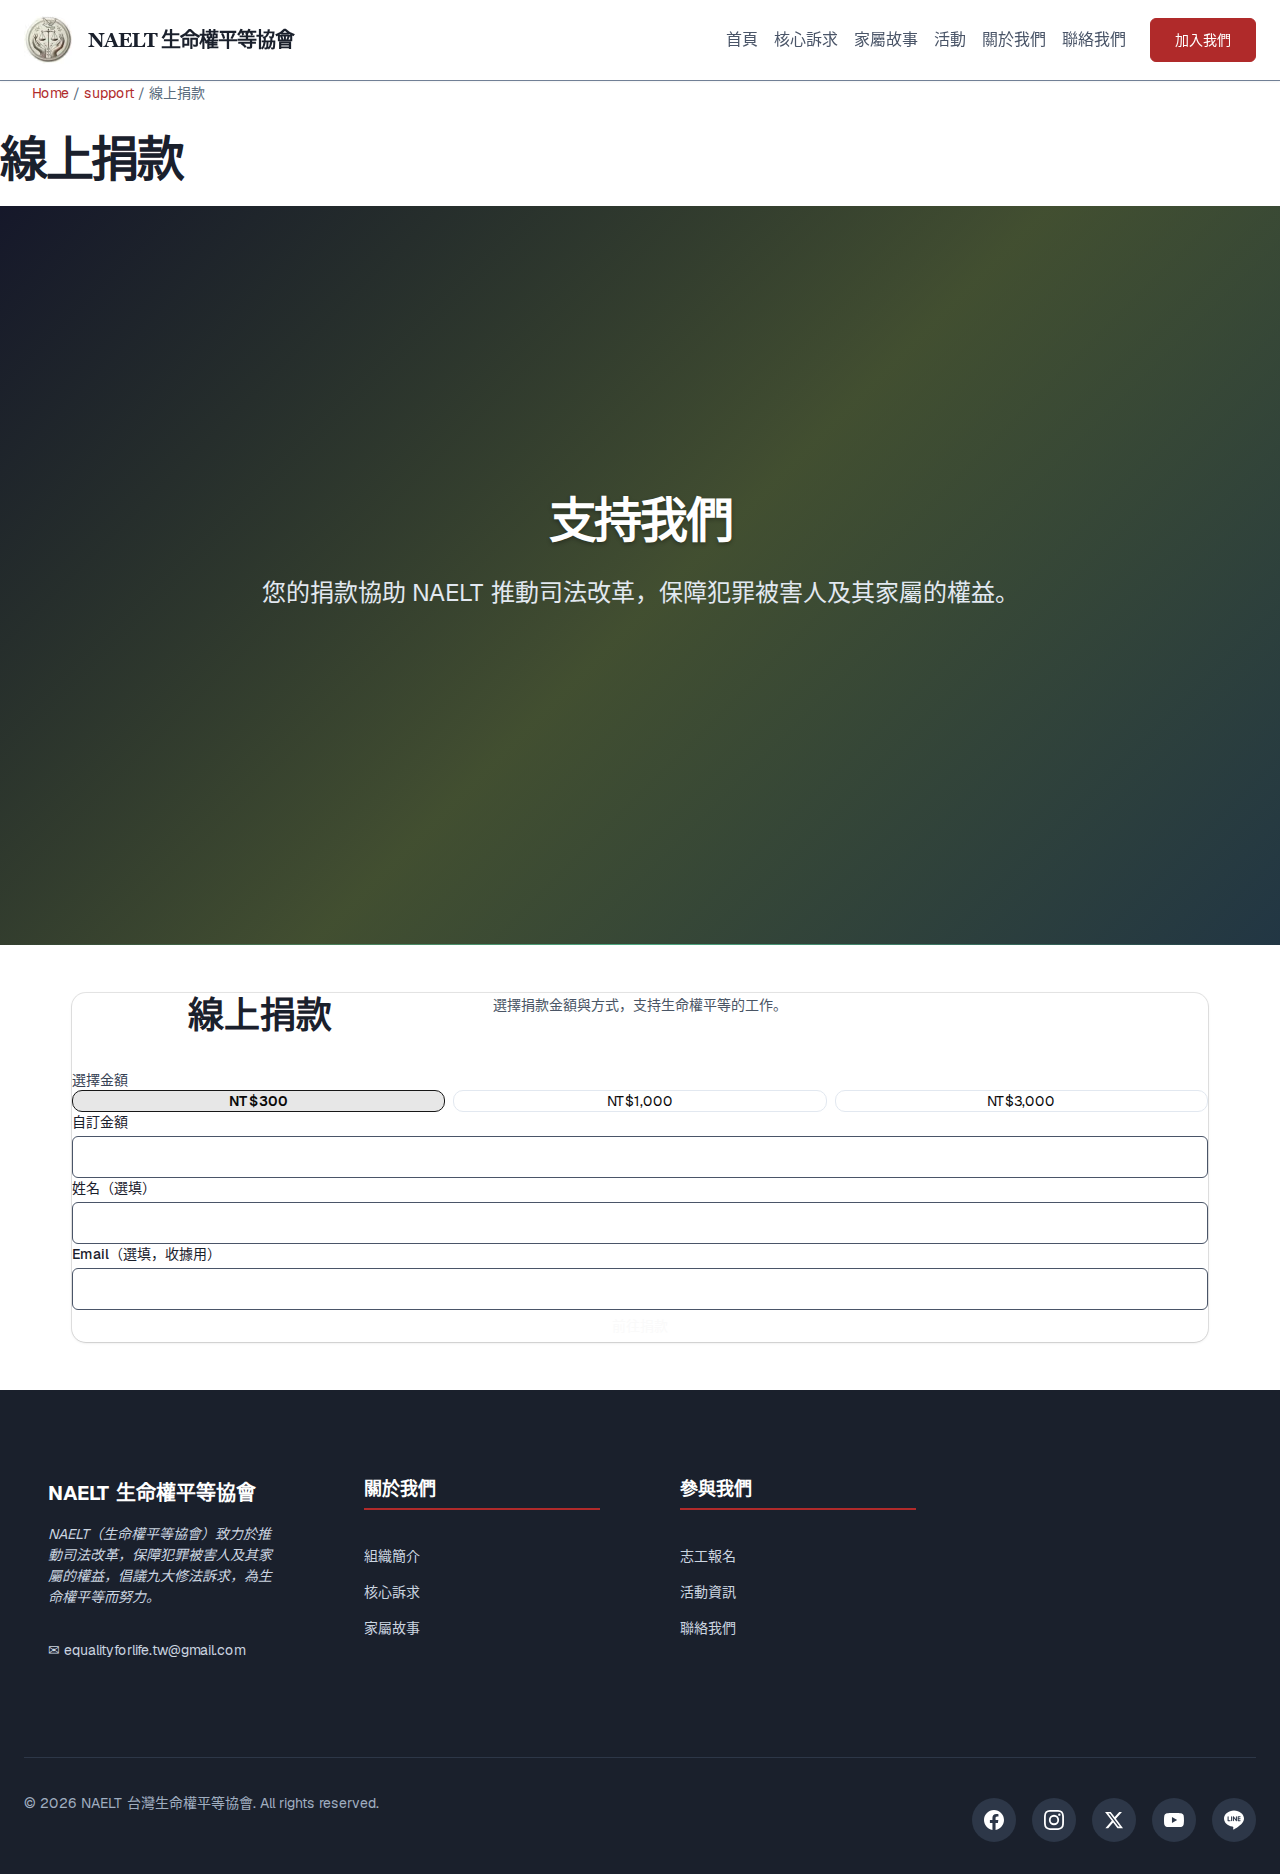
Public createPaymentCheckout(purpose) + a provider-registry (add a driver = one blank import) + a single PAYMENT_MODULE_ENABLED mount switch (ADR rejecting a runtime .so). Per-site BYOK secrets (write-only, masked-on-read), per-site routed sessions (VIP DB / non-VIP D2 RLS), order/line-item + product/service/variation/category catalog, and digital entitlements auto-granted on paid.
Proof tier: unit / property (gopter + fast-check) / mutation / enttest + web vitest + cms mocked-GraphQL component + tsc + governed browser-full-integration (both tiers). Not live external provider/OAuth/settlement, real charge/invoice, DNS/TLS/deploy, UAT, or production. Authority: .agents/specs/payment-plugin/review.md, PR #86.
A backend/config-tier hardening lane shipped as PR #71 against dev, promoted from a repo-wide mock/stub/false-green audit (prod-readiness-wireup-hardening). These are shipped fixes (cited to PR + spec evidence), not roadmap; no new screenshots were captured, so the visuals on this page still stand.
Tenant database connections could previously fall back to default credentials and non-TLS in production. They now reject default user/password and require TLS when ENV=production — closing a fail-open path that the central platform-DB validation did not cover. 6 unit tests + 2 hand-killed mutants.
The CMS no longer sources provider keys from NEXT_PUBLIC_*_API_KEY (which would inline secrets into the browser bundle); generation routes through the backend BYOK path, and the admin endpoint fallback fails closed on Vercel-style production markers.
An empty placeholder test was replaced with a real-dependency chaos test: the production health checker against a downed Postgres returns HTTP 503 (unhealthy), bounded — the most central dependency now has executable fail-closed evidence instead of mock-only coverage.
Module guides that under-stated implemented OAuth (Google/Facebook/Microsoft/Cognito + SAML + LDAP), storage (S3/GCS/Azure/R2/local), and real GraphQL data-binding were corrected — so the genuine remaining gaps stand out instead of being hidden behind stale "TODO" notes.
A new resilience cluster proves the platform stays bounded and never hangs under fault injection: connection-pool exhaustion stays within its limit and recovers; a transient tenant-DB outage isn't cached and routing self-heals; a hung AI provider fails with a bounded typed error. Runtime-backed on governed PostgreSQL + hand-killed mutants.
The user-input→tenant-ID/cms_<slug> database-name sanitizer and the production credential/TLS guards gained property-based (gopter/fast-check) + call-site-wiring tests, so a future refactor can't silently weaken the only sanitizer before a DB name or re-open an insecure connection path.
The spec-governance artifacts were token-lean'd while keeping full traceability: ISSUE_LOG.md 270→65, NEXT_STEPS.md 5654→63, RTM.md 2789→382, SPECS.md chars −59% — the complete catalogs/indexes stay in the active files; full history moved verbatim to *_ARCHIVE.md. Open items reconciled to 4, all owner/infra/docs-gated.
After the 2026-06-16 capture below, two backend/API-tier lanes shipped as PRs against dev. Both are shipped capabilities (cited to PRs + spec evidence), not roadmap; no new screenshots were captured, so the visuals on this page still stand.
A spawned VIP site is no longer a dangling control-plane record: SpawnSite now creates the physical cms_<slug> database and migrates the schema into it (the create-side gap that previously forced hand-creating cms_showcase). Non-VIP/D2 stays record-only by design; fail-closed with site-record rollback. Proven by unit + property + 8 hand-killed mutants + a governed-PostgreSQL integration test.
The two previously-stubbed GraphQL operations are now implemented: updatePostDraft (edit a draft pre-publish; a published post is immutable) and upsertSkillTemplate (create / version-bump), both gated on site.social.manage. Includes a gqlgen codegen-hygiene refactor so schema regen stays safe.
CMS Platform is a multi-tenant, DB/config-driven CMS with a Go backend, Next.js CMS admin, public web, plugin architecture, AI/SEO surfaces, and governed spec/test evidence. The 2026-06-16 pass refreshed the stakeholder artifacts after the non-VIP tenancy model converged on D2 (shared-table RLS) per ADR-RLS-002, the deprecated schema-tier code was removed, and host-preflight/operator tooling shipped — with the full local stack up on real data/API and fresh evidence.
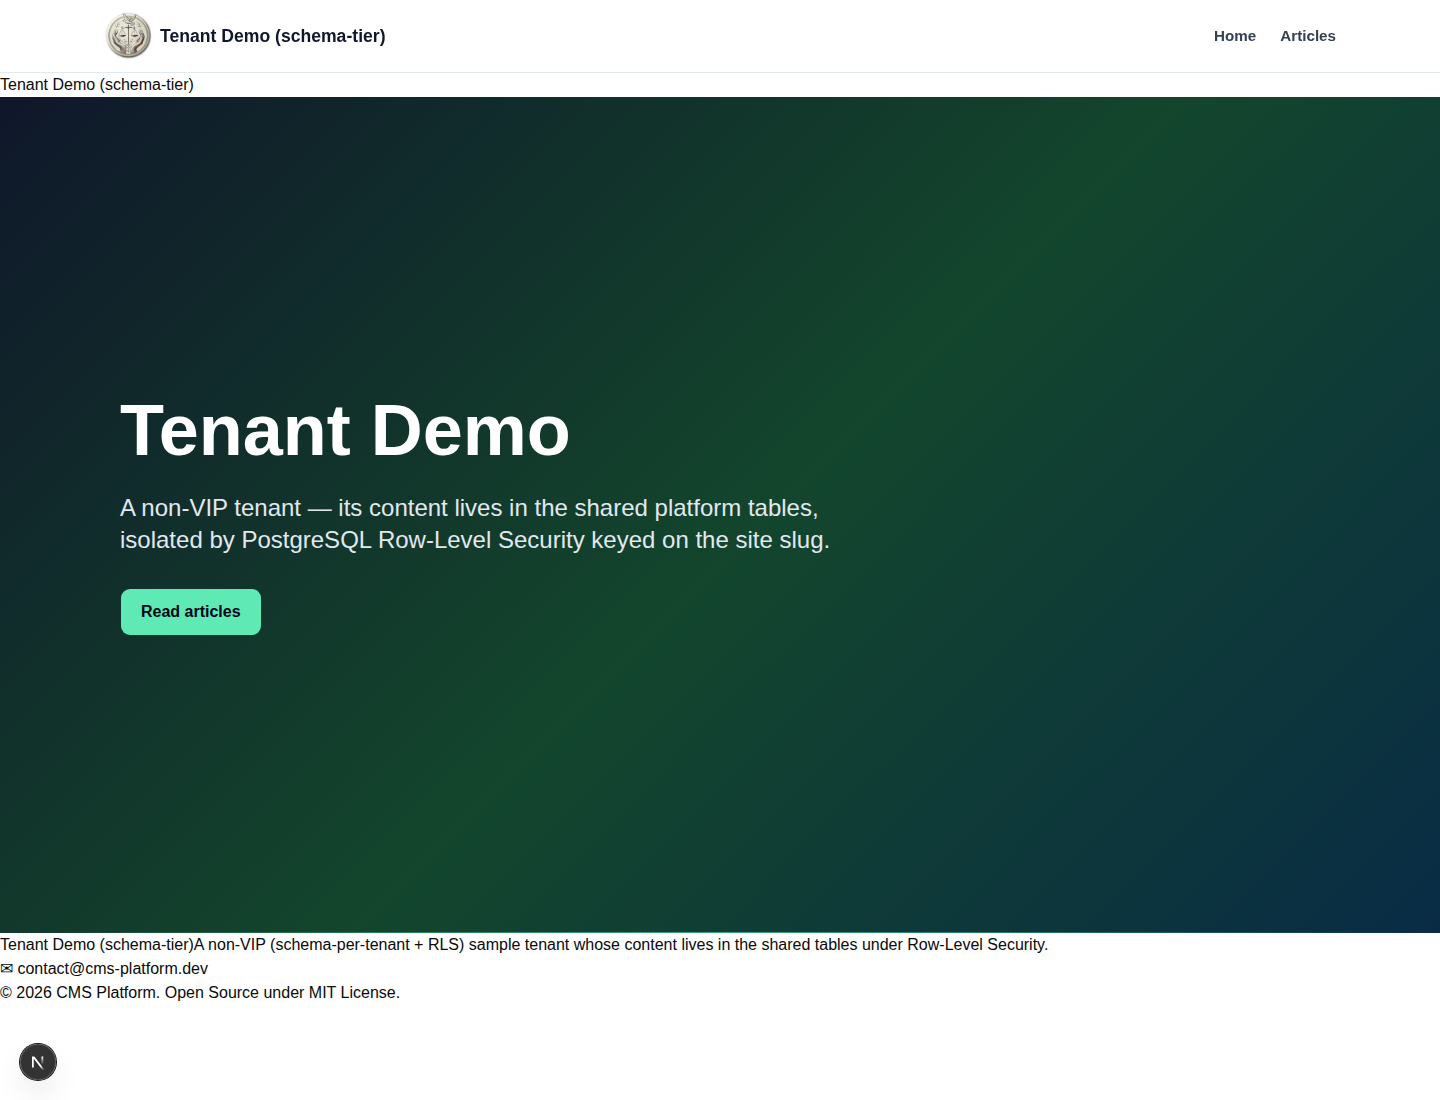
VIP ⇒ database-per-tenant; non-VIP ⇒ shared-table RLS (the "D2" model). Four seeded sites now make both tiers visible: three DATABASE/VIP sites plus tenant-demo on the SCHEMA/non-VIP tier, each rendering identically to the end user.
The non-VIP read path is proven on a governed PG15 from primitives → provider → real public MCP read tools → literal HTTP transport, as a genuine non-superuser role, plus a transaction-pool safety proof. A host-capability db-doctor + a one-command provisioning flow make host selection reproducible.
Cloud Run runtime is live and Cloud SQL RLS is wired; custom-domain browser proof, public-domain /mcp proof, worker, AGE/GraphRAG, multi-region, and UAT are still not claimed.
Since the 2026-06-15 PR #9 review. Items below are backed by spec-local review.md / tasks.md / ADR evidence cited in the Source Manifest.
Owner-approved: non-VIP tenancy is shared-table Row-Level Security keyed on the site, enforced by a non-superuser app role. The deprecated schema-per-tenant/search_path code (provider, router, middleware, per-schema rollout) was removed; one model, one rollout (rls-rollout-shared).
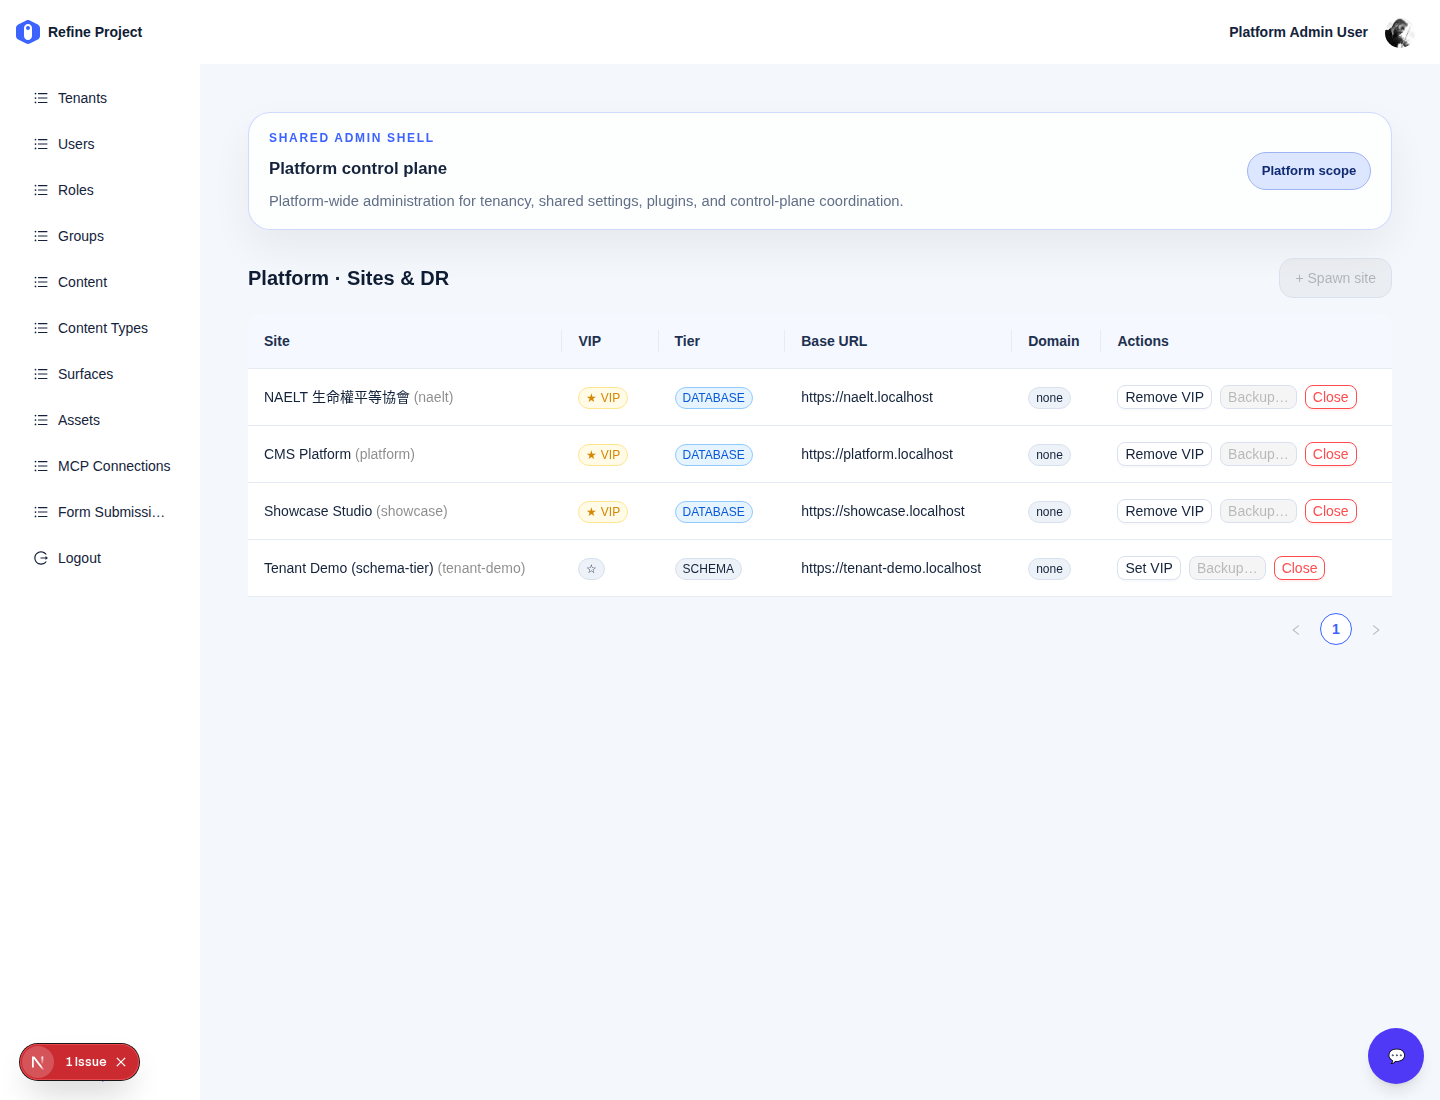
A fourth seeded site tenant-demo (tenancyTier:schema) renders as a public site at /site/tenant-demo and appears in the DR admin "Sites & DR" table with the SCHEMA badge and a Set VIP action (vs Remove VIP for DATABASE sites) — closing the prior "seed only exercises VIP tier" gap.
migrate db-doctorA read-mostly probe for any candidate Postgres: can it create a non-superuser app role and have FORCE RLS actually confine it, and does it have pgvector + Apache AGE for runtime GraphRAG (advisory)? Turns host selection from a guess into a reproducible check; runtime-backed on a governed PG15.
A one-command idempotent provision→seed→rollout→verify script (with --dry-run + a documented env contract), a post-deploy /mcp cross-tenant UAT smoke, and a proof that D2 is safe behind a transaction-mode PgBouncer (SET LOCAL is tx-scoped) + default-OFF PgBouncer Helm values.
Each card shows Evidence Source, Coverage Tier, and claim boundary directly in the artifact.
migrate db-doctor$ migrate db-doctor ✅ privileged-role-can-create-app-role ✅ app-role-is-non-superuser ✅ app-role-non-bypassrls ✅ force-rls-confines-app-role ⚠️ tls NOT using TLS — set sslmode=require ⚠️ extension:age NOT available — GraphRAG cannot run here ⚠️ extension:vector NOT available — GraphRAG cannot run here ✅ HOST OK for the D2 shared-table-RLS read path.
Questions leadership and operators should ask before treating Cloud Run runtime as full launch approval.
It proves Cloud Run runtime is live and Cloud SQL shared-table RLS is wired, but it does not prove custom-domain browser behavior, public-domain /mcp cross-tenant isolation, worker runtime, AGE/GraphRAG, multi-region, or UAT sign-off.
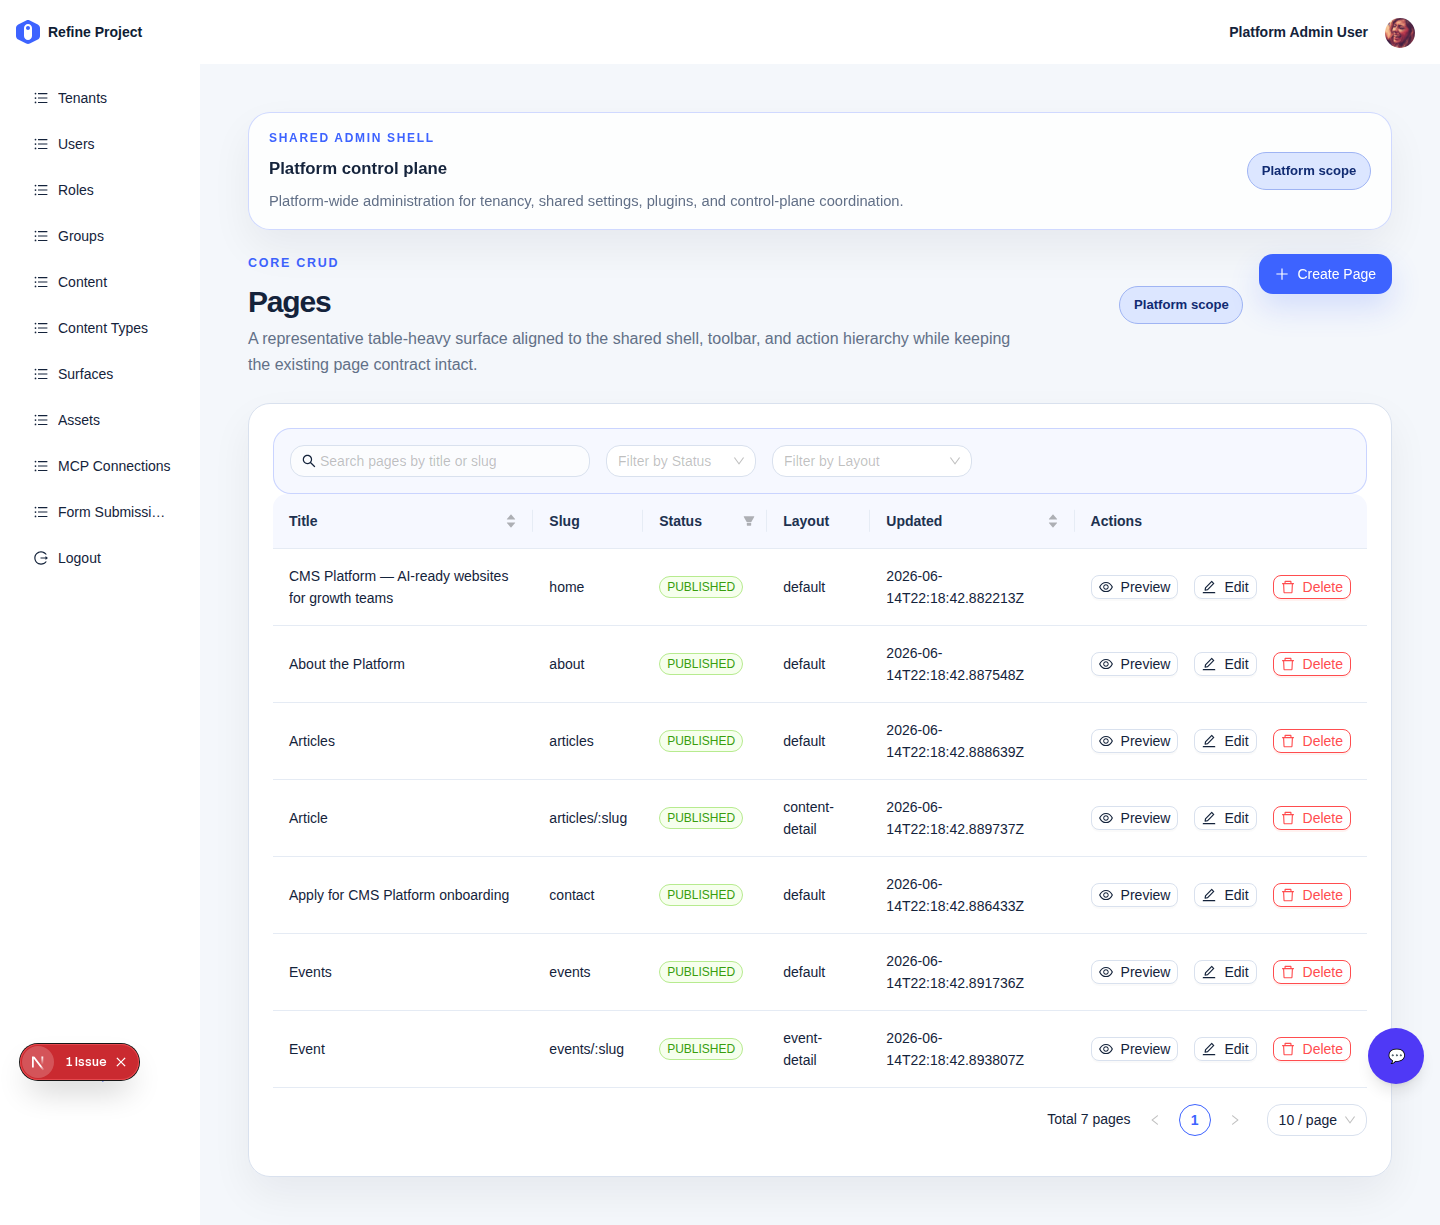
Backend GraphQL returned 4 seeded sites — platform, naelt, showcase (DATABASE/VIP) and tenant-demo (SCHEMA/non-VIP). The DR admin table renders all four backend-backed; the non-VIP site renders publicly at /site/tenant-demo.
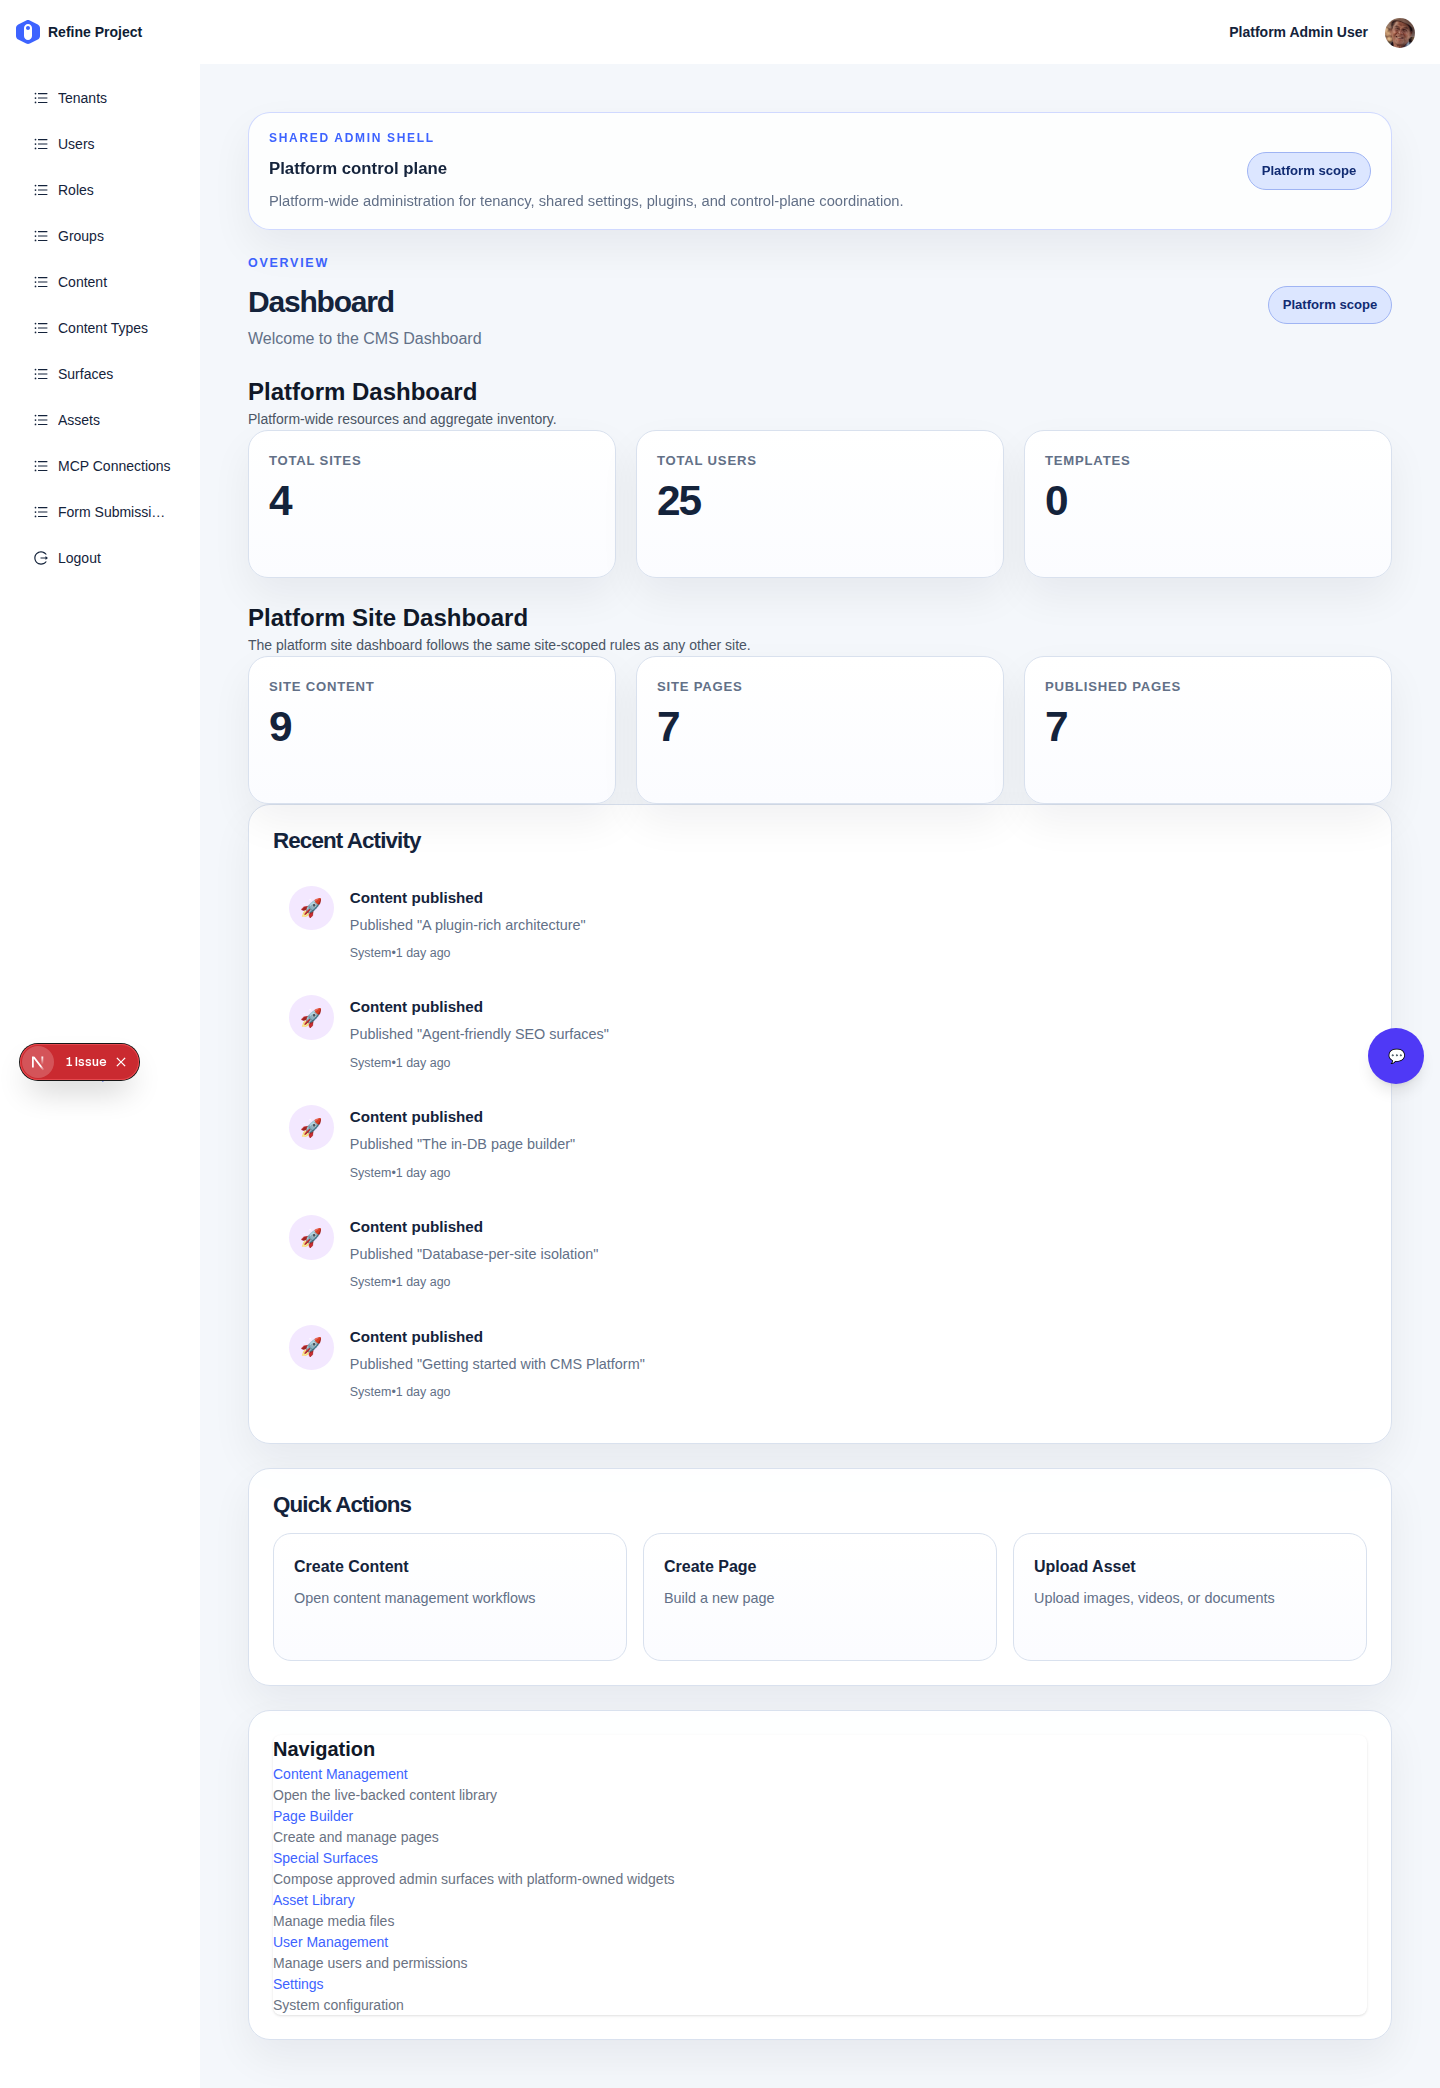
The non-VIP tier is now exercised, but all four sites set domain none, so the pending-custom-domain Verify affordance and the per-tenant /settings/dr panel are still not seed-exercised; backup/spawn render disabled (unbuilt). CMS captures are hybrid auth with a Next dev "1 Issue" overlay badge.
Yes — runtime-backed end-to-end on a governed PG15: primitives → provider → real public MCP read tools → literal HTTP transport, as a non-superuser role, default-off via SCHEMA_TIER_APP_USER. What is NOT done is confirming /mcp over the public custom domain after certificates finish provisioning.
CMS captures used the real CMS runtime plus CMS auth API cookie bootstrap. That is hybrid evidence and must not be described as full browser-login.
The non-VIP model converged on D2 (ADR-RLS-002) and the deprecated schema-tier code was removed; a non-VIP seed site now exercises the SCHEMA tier visually; and a host-preflight db-doctor + turnkey operator flow + PgBouncer transaction-pool safety shipped.
Full local stack up on real data/API, capped to the evidence actually gathered (2026-06-16).
Seed 4 sites (platform, naelt, showcase = DATABASE/VIP; tenant-demo = SCHEMA/non-VIP)
  -> Stack up: backend GraphQL :28080 (HTTP 200, 4 seeded sites), CMS :23000,
     web :23001, postgres :5432, valkey :6379
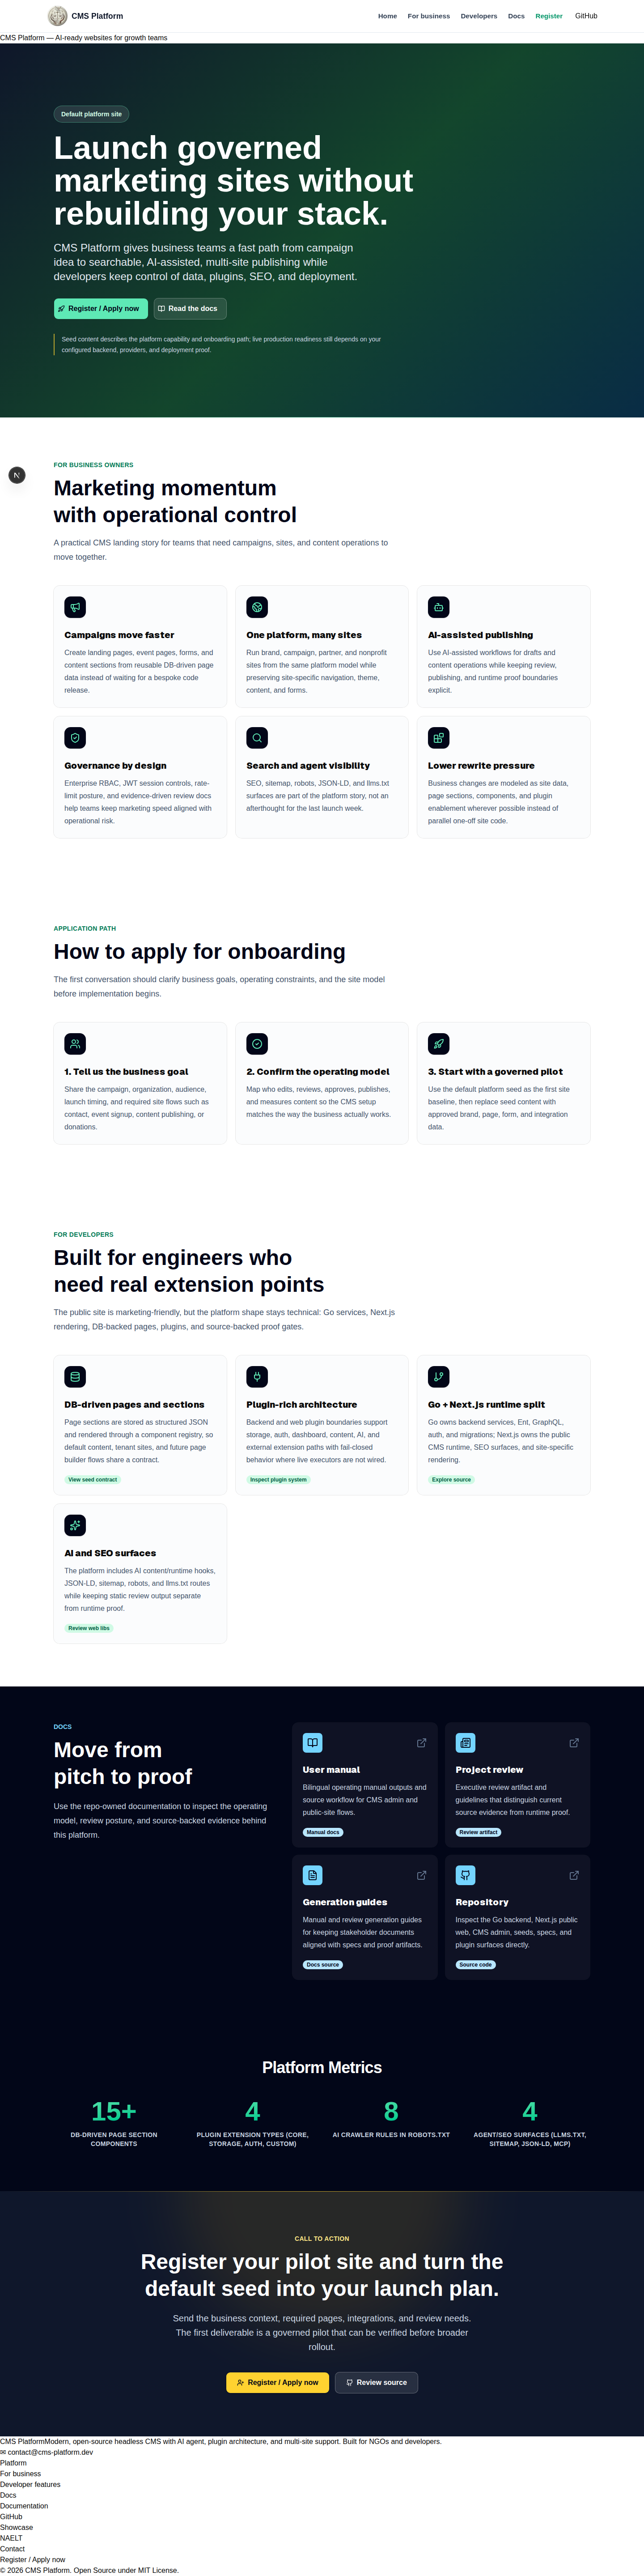
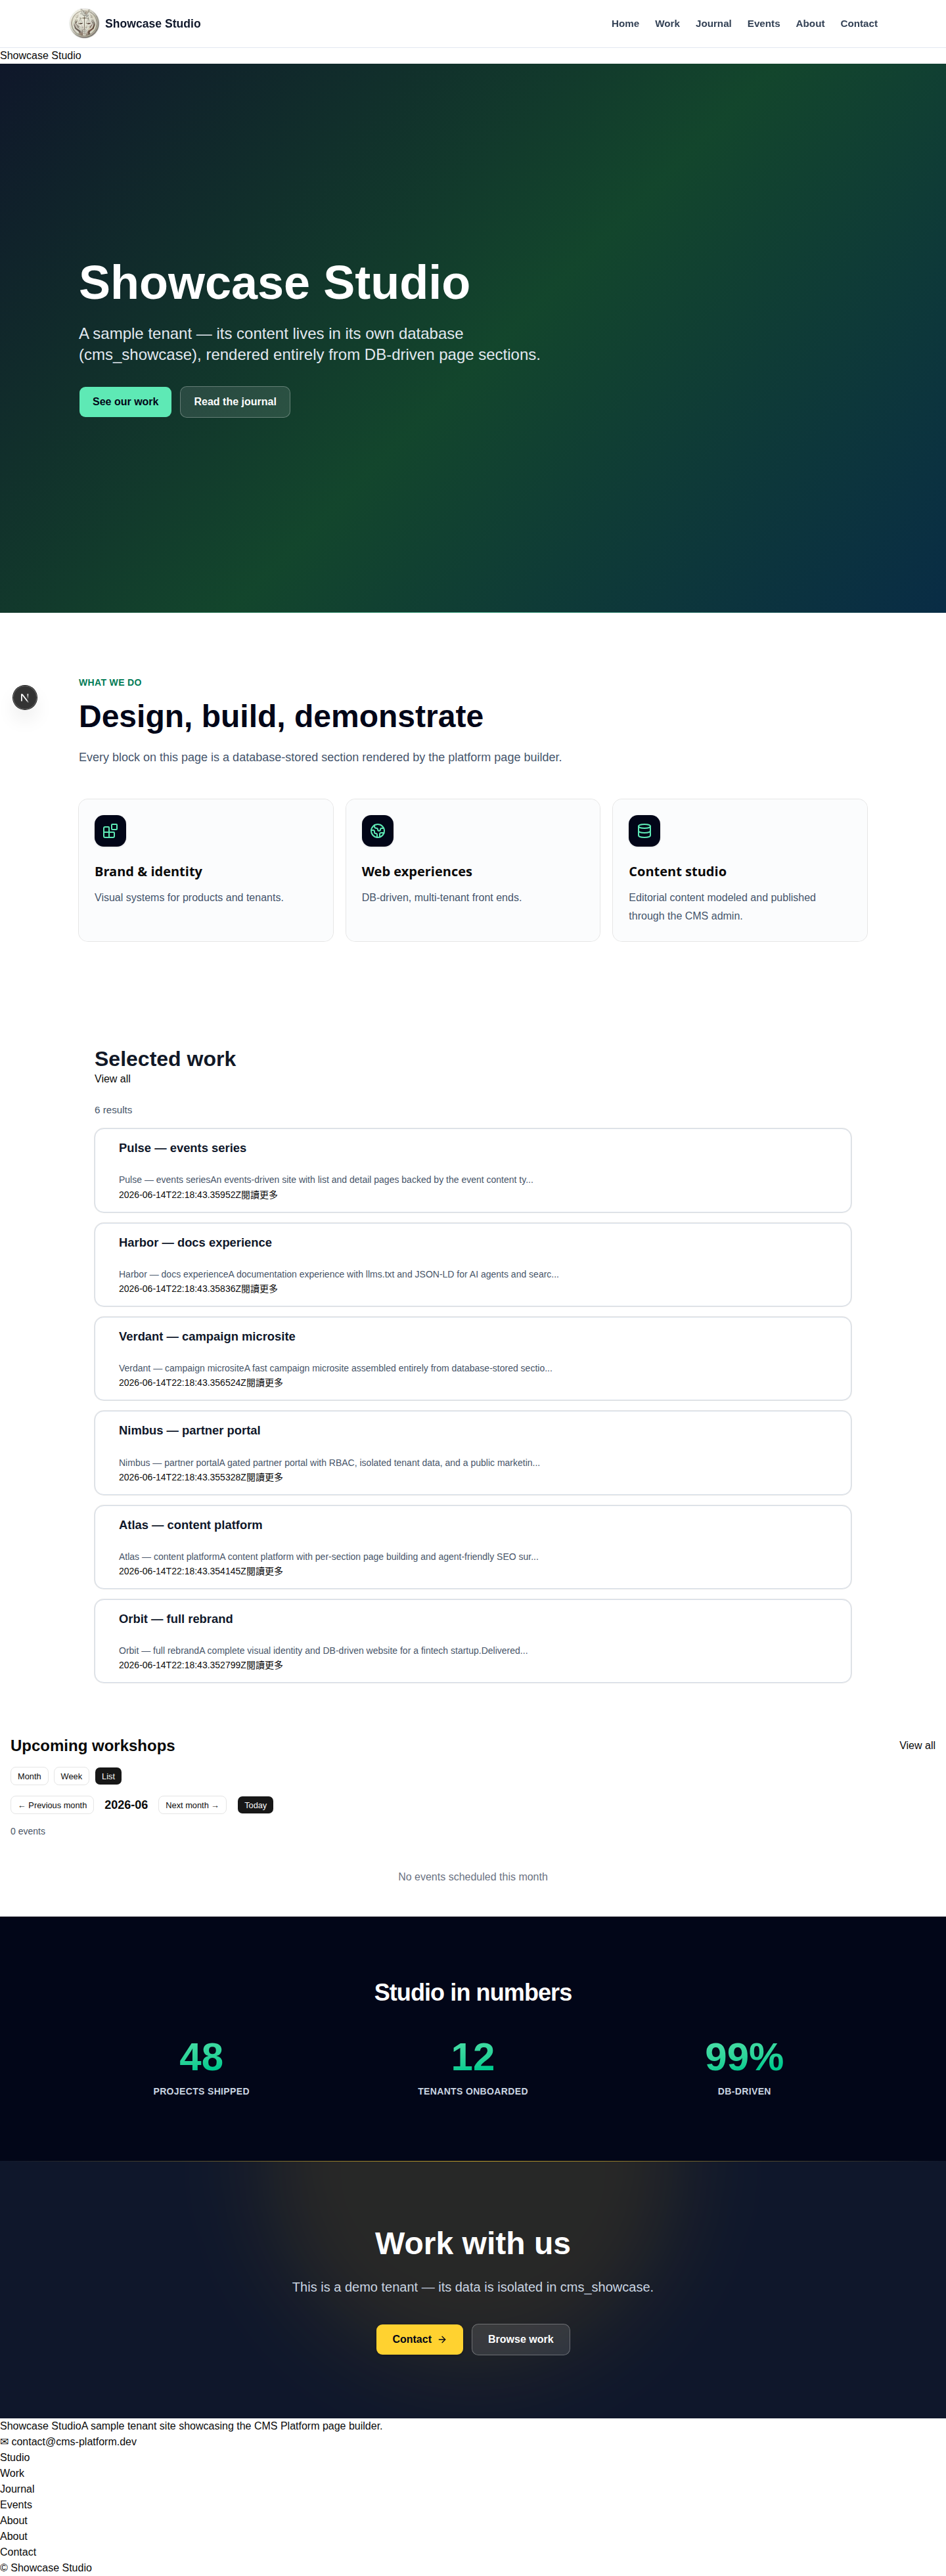
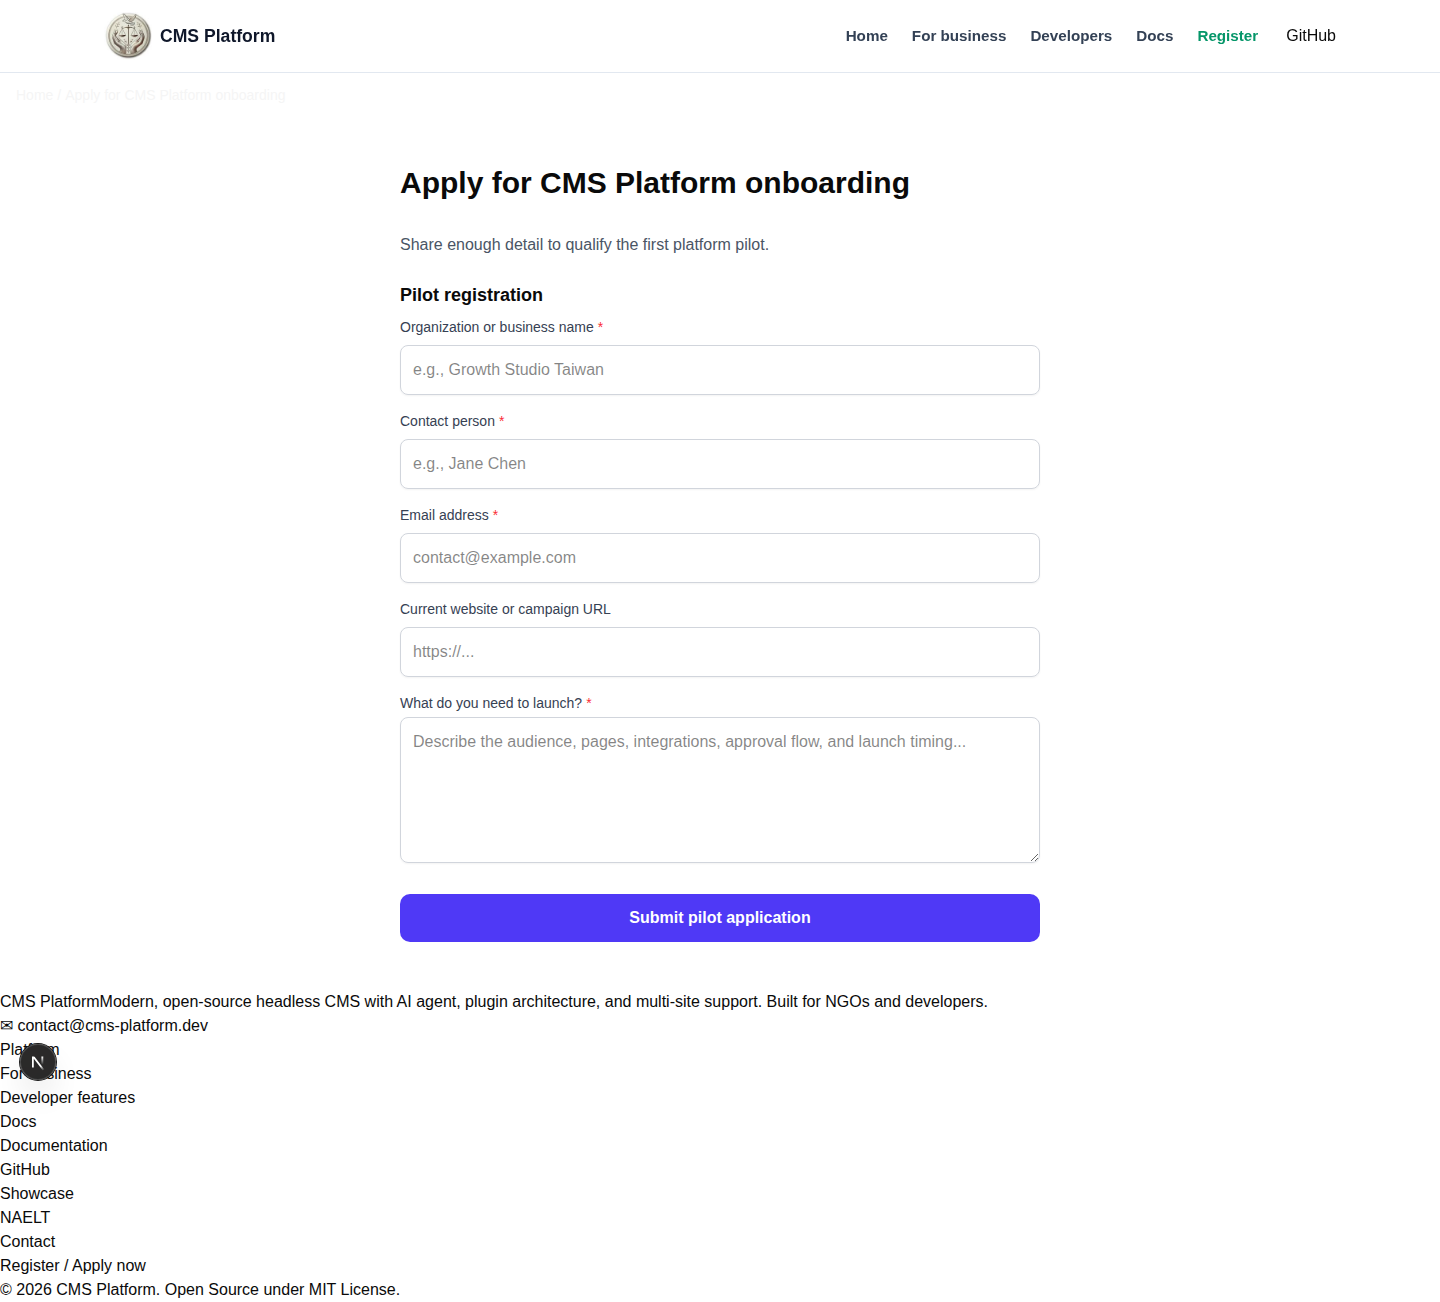
  -> Public routes 200: /site/platform, /site/platform/contact, /site/naelt,
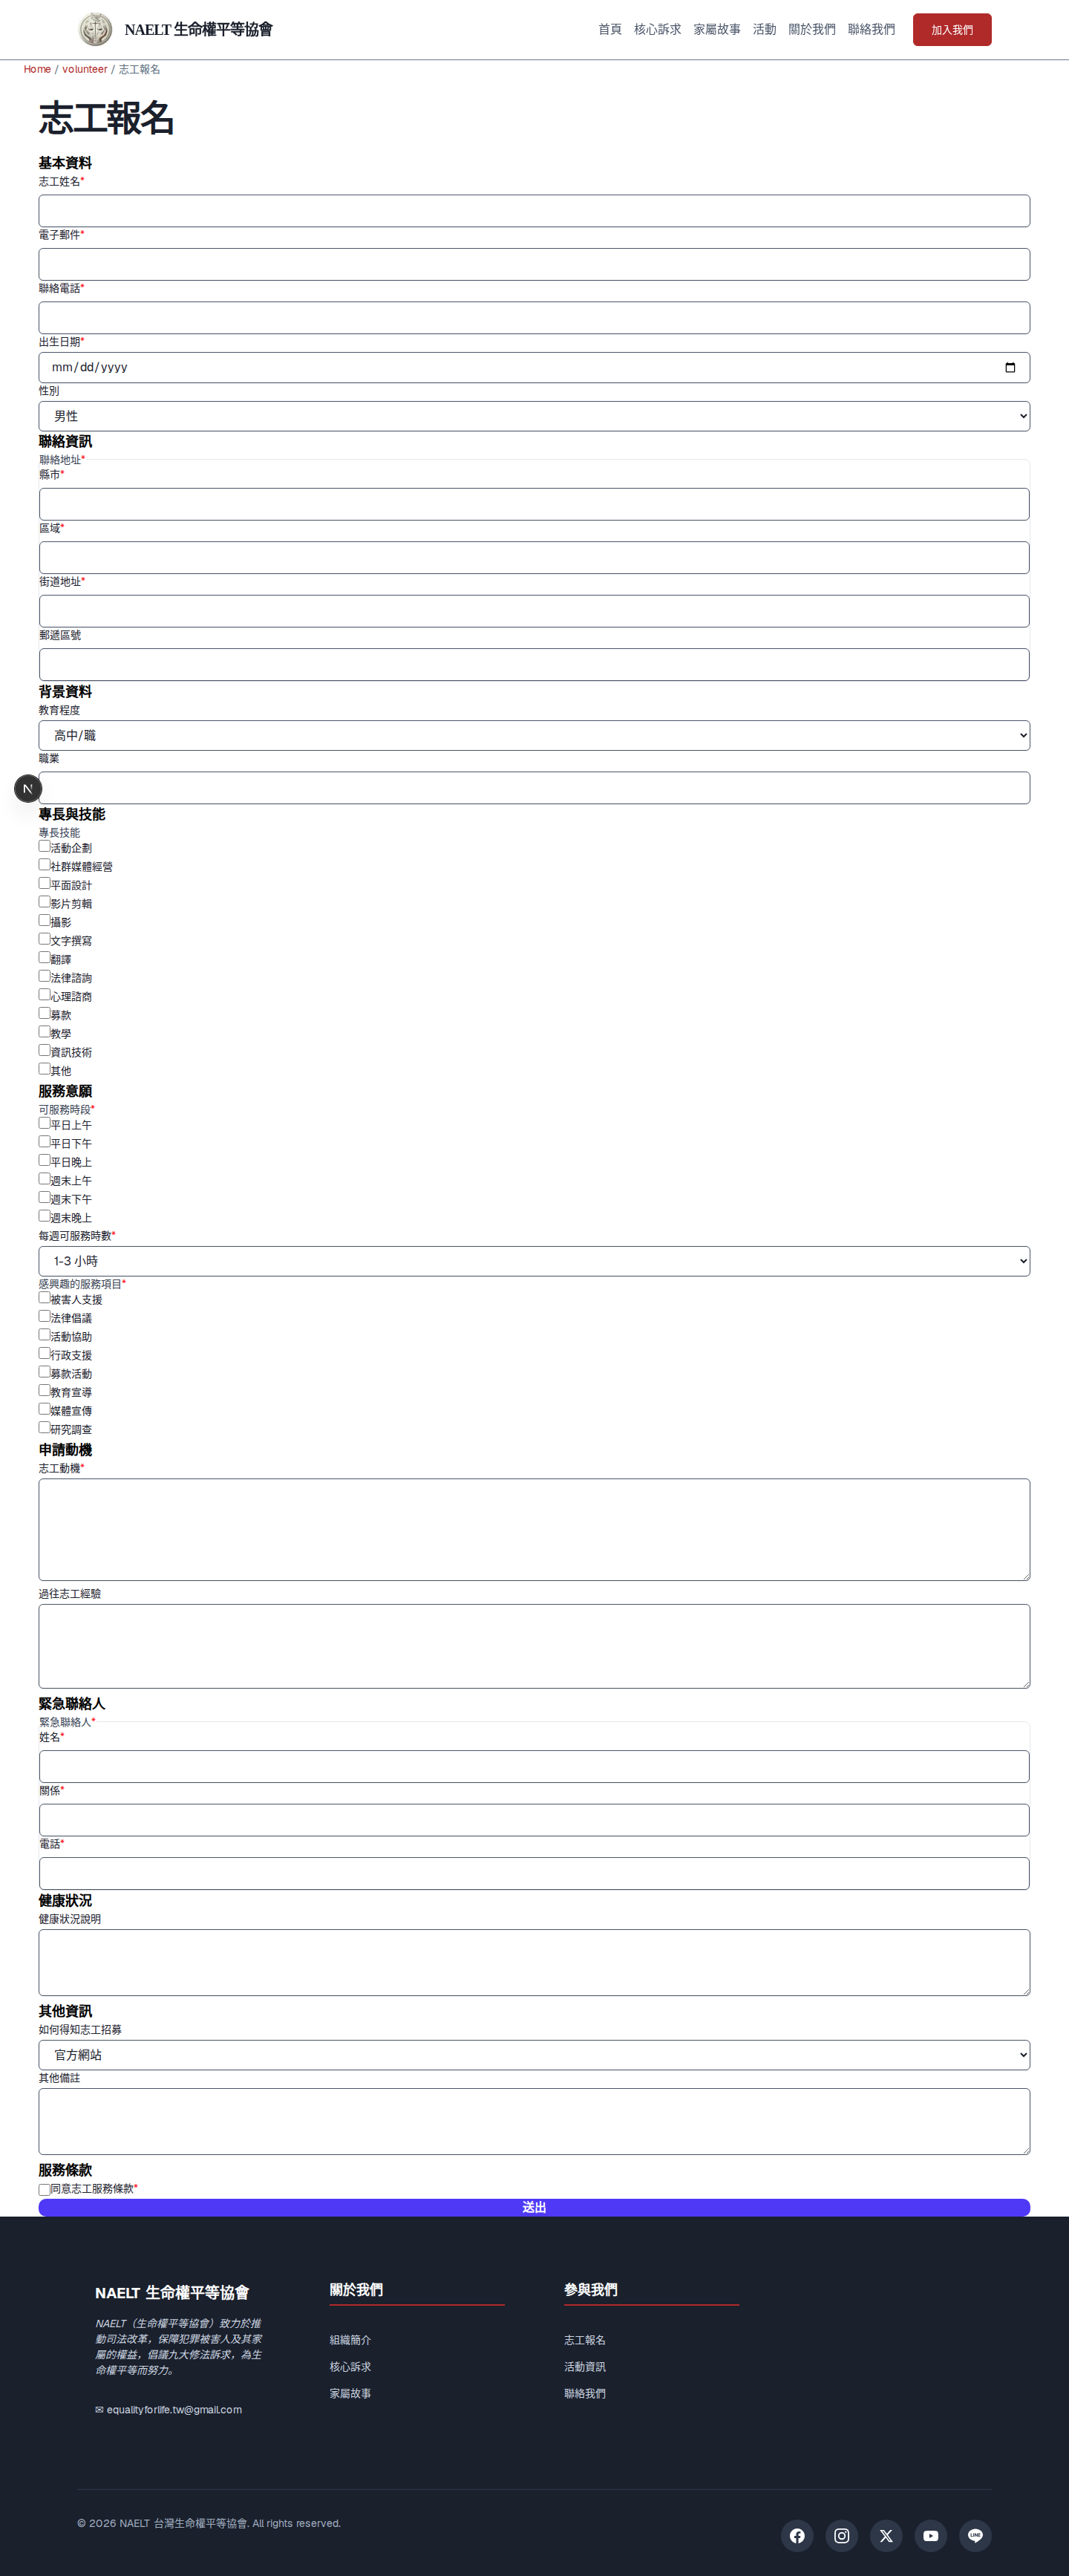
     /site/showcase, /site/tenant-demo, /site/naelt/volunteer/register
  -> DR admin /platform/sites renders backend-backed: 4 sites, 1 SCHEMA/non-VIP row
  -> Host preflight: `migrate db-doctor` PASS on governed PG15 (non-super + FORCE-RLS
     confined; pgvector/AGE advisory-absent); `provision_...py --dry-run` plan printed
  -> Fixed scripts/ops.py db seed (broken single-file go run after migrate pkg split)
  -> 9 fresh screenshots + 2 CLI transcripts captured under docs/{manual,review}/assets/
-> Production final gate remains blocked until DNS/TLS + deploy + UAT + hosted DB existResolved items are real improvements since the prior review; open gaps remain bounded and should not be marketed as complete.
tenant-demo on the SCHEMA tier, so the DR admin SCHEMA badge + Set-VIP distinction render with real data and the non-VIP public site loads (closes the top visual gap from 2026-06-15; ISSUE_LOG DR-DEMO-SEED-COVERAGE-001, partial)./mcp (default-off).db-doctor (incl. pgvector/AGE detection), --dry-run + env contract, post-deploy UAT smoke, PgBouncer transaction-pool safety + Helm.scripts/ops.py db seed corrected to go run ./cmd/migrate (the single-file invocation broke after the migrate package split).CMS Platform now demonstrates both tenancy tiers end-to-end: a VIP database-per-tenant site and a non-VIP shared-table-RLS site render identically, while a host-capability preflight and a one-command provisioning flow make standing the non-VIP path up on a new Postgres a reproducible, verifiable operation. The next milestone is not more local proof; it is production-domain closure — certificate-complete browser proof, public-domain /mcp cross-tenant proof, UAT, and later worker/AGE/GraphRAG/multi-region decisions.
All four seeded sites set domain none, so the pending-custom-domain Verify affordance and the per-tenant /settings/dr panel are still not visually exercised; backup/spawn ops render disabled (unbuilt).
CMS captures (dashboard, page builder, DR admin) use auth-cookie bootstrap — hybrid evidence, not full browser-login. A Next dev "1 Issue" overlay badge appears.
No full backend-backed CMS browser e2e exists yet for the DR admin UI; the table is shown via backend-backed capture, not an automated browser suite.
The live Cloud SQL RLS layer is provisioned and wired, but the public custom-domain /mcp cross-tenant proof still waits for the API certificate and at least two non-VIP tenants.
The Cloud Run HTTP services are live; continuous worker runtime, AGE-backed runtime GraphRAG, and multi-region/HA expansion remain deferred decisions.
Cloud Run runtime and DNS mappings exist, but Google-managed certificates were still provisioning during this pass; custom-domain browser proof and UAT are not claimed.
After certificates finish, verify www, admin, and api end-to-end, then run the /mcp cross-tenant UAT smoke against the public API URL.
Decide and implement worker runtime, AGE/GraphRAG, multi-region/HA, and any remaining production backup/restore drills.
Run the launch/UAT matrix against production values and keep proof-tier labels separate from local predecessor screenshots.
Used sources are explicit through the 2026-07-11 documentation-governance pass. No docs/*FEATURE*.md exists in this repo, so the spec/report/IaC chain below is the fallback authority. RTM.md is rollup only, not readiness authority.
| Source | How it was used |
|---|---|
.agents/specs/{SPECS,NEXT_STEPS,ISSUE_LOG,RTM}.md (through 2026-07-11) | Spec registry, rolling queue, issue-first launch notes, and traceability rollup; the 2026-07-11 pass uses them only for doc-governance context, not new runtime proof. |
docs/SHOWCASE_GENERATION_GUIDE.md | Audience split and source-manifest rules for the docs hub/showcase surface, plus manual/review quick-link maintenance. |
.agents/specs/production-deployment-topology/{review.md,adr/ADR-DEPLOY-003-gcp-cloudrun-cloudsql-cloudflare.md} + infra/terraform/envs/gcp-cloudrun/ | Production deployment authority: Cloud Run runtime live on run.app, Cloud SQL/Upstash connectivity, Terraform IaC, and live shared-table RLS provisioning/wiring claim boundary. |
.agents/specs/schema-per-tenant-routing-rls/{tasks.md (Slice 8), review.md, adr/ADR-RLS-002-NON-VIP-CANONICAL-D2.md} | The D2 canonical model + host-preflight / dry-run / UAT-smoke / transaction-pool-safety deliverables and their claim caps |
.agents/specs/tenant-lifecycle-dr-admin/{design-cms-ui.md,requirements.md,tasks.md} | DR admin UI scope (no review.md in this spec dir; cites the design/requirements/tasks chain) |
backend/seeds/{platform,naelt,showcase,tenant-demo}-*.json | Canonical seed/demo/sample data for the 4 seeded sites (the new tenant-demo carries tenancyTier:schema) |
| Live runtime probes (2026-06-27 deployment pass) | Backend GraphQL 200 in prd on Cloud Run with Cloud SQL socket + Upstash TLS connected; cms/web healthy on run.app; live Cloud SQL shared-table RLS provisioned and verified. Existing 2026-06-16 local route screenshots remain predecessor visual evidence. |
docs/review/assets/*-review-2026-06-16.png + *-cli-2026-06-16.txt | 9 predecessor 2026-06-16 local screenshots + 2 CLI transcripts embedded in this artifact; no new screenshots in the 2026-07-11 documentation-governance addendum |
docs/{REVIEW_GENERATION_GUIDE,PROJECT_REVIEW_GUIDE,REVIEW_AND_DOCS_GUIDELINES,MANUAL_GENERATION_GUIDE}.md | Review/manual workflow, capture rules, source-manifest rules, and project-specific review priorities. |
docs/*FEATURE*.md | No matching files exist in this repo; fell back to the spec/report chain above. |
docs/*SPEC*.md | Matching docs-spec files are historical/secondary context; active spec artifacts and RTM remain the readiness authority. |